

4
min read

September 17, 2026
Why AI Safety is Your New Competitive Edge
Many enterprise AI projects encounter delays or fail to launch, often due to a fundamental concern: the risk of "AI extraction." This refers to the potential for proprietary business logic or sensitive data to be reverse-engineered or inadvertently exposed by an AI model. While leaders recognize the transformative potential of Generative AI, this risk can keep ambitious initiatives confined to the pilot phase.
At iForAI, we approach safety not as a mere compliance task but as a strategic enabler. By establishing trust in AI systems, organizations can accelerate their innovation and deployment efforts.
The Shift from Experimentation to Enterprise-Grade Security
The initial phase of experimenting with public, general-purpose AI models is evolving. To achieve measurable return on investment (ROI), enterprises must integrate these models with their internal, sensitive data—such as customer histories, supply chain logistics, and intellectual property.
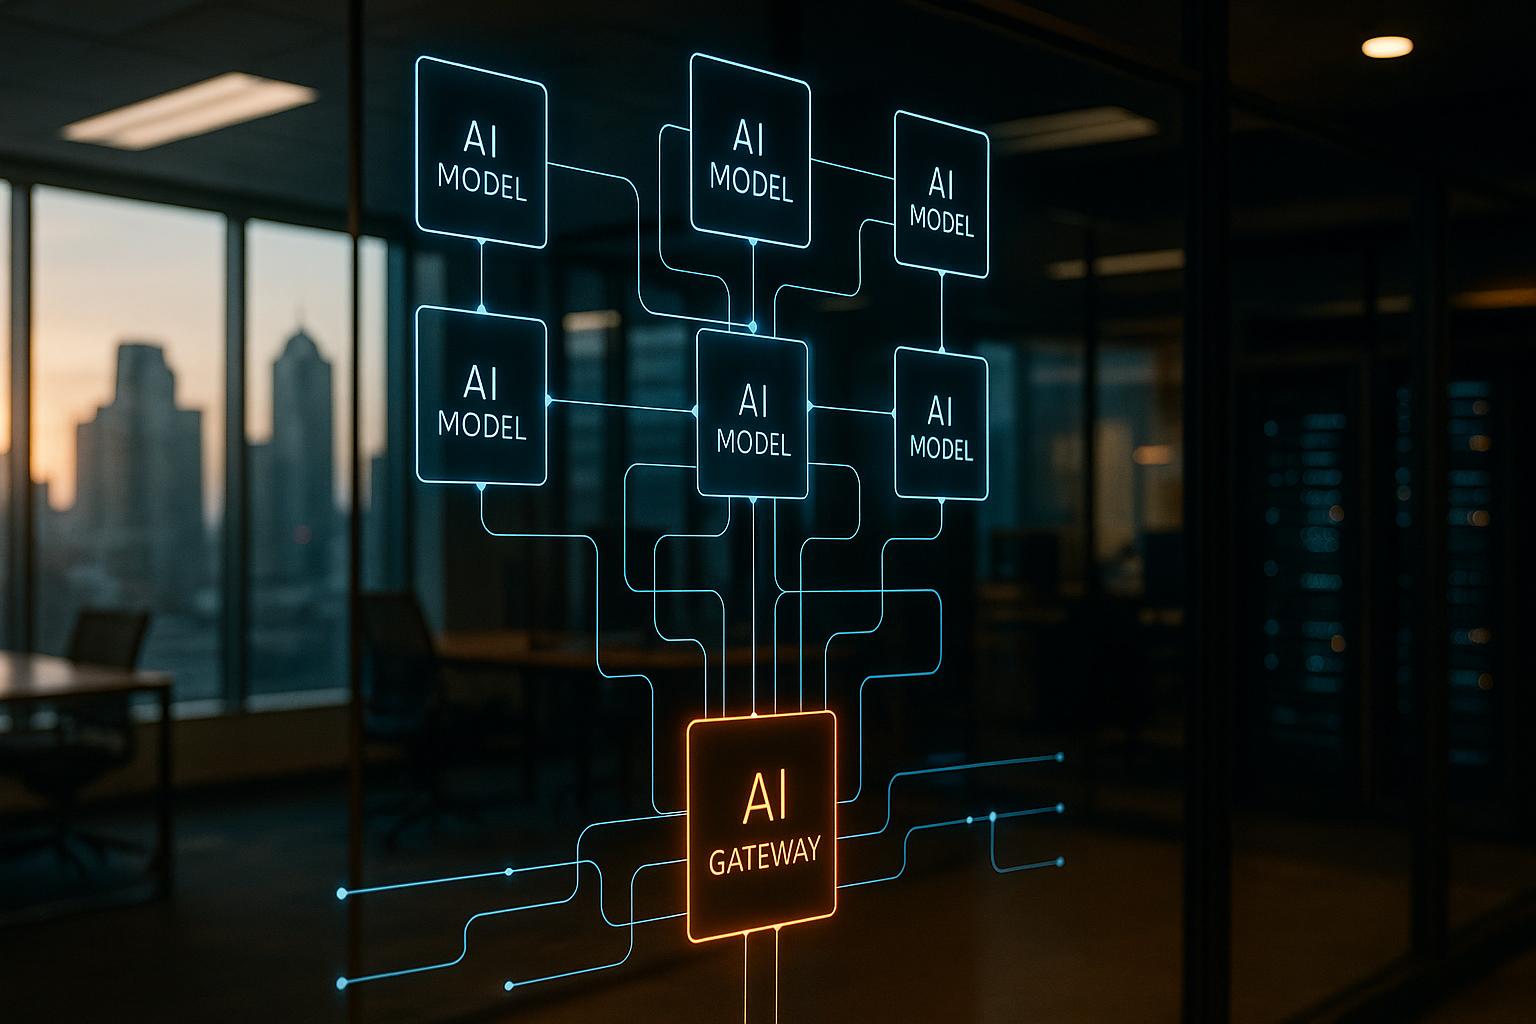
However, feeding sensitive data into an unprotected model can create immediate infrastructure vulnerabilities. Without a robust, secure data layer, an application can become a significant liability. Enterprise-grade AI necessitates moving beyond experimental environments into structured architectures where data protection is integral from the outset.
The RAG Security Gap: Why Basic Implementations Are Insufficient
Retrieval-Augmented Generation (RAG) is a widely adopted method for connecting large language models (LLMs) to private data sources. A critical challenge with many generic RAG implementations, however, is their lack of integration with user permissions.
For instance, if a junior analyst lacks authorization to view executive payroll data in an Enterprise Resource Planning (ERP) system, an AI agent should similarly be prevented from accessing and summarizing that information for them. Effective enterprise AI requires an engineering-first approach that embeds existing Identity and Access Management (IAM) protocols directly into the AI workflow. Securing the prompt is one aspect; securing the data retrieval path is equally, if not more, crucial.
Security as a Competitive Advantage in AI Scaling
Organizations that perceive governance as an obstacle may find themselves in a cycle of perpetual experimentation. Conversely, leaders who prioritize secure, specialized workflows can develop a "value protector"—a core component of their intellectual property.
By integrating governance into the development lifecycle, organizations can gain the confidence needed to scale their AI initiatives. While some competitors may face delays due to risk assessments or data breaches, a secure infrastructure allows for the deployment of AI agents capable of handling high-stakes business processes.
Moving from Stalled Pilots to Operational Excellence
The transition from conceptual AI to real-world ROI is facilitated by robust infrastructure. AI extraction is a tangible risk, but it can be mitigated through rigorous safety audits and thoughtful engineering practices.
Key Takeaway: Do not allow infrastructure limitations or security concerns to impede innovation. By proactively addressing trust and security, organizations can move from conceptual AI projects to operational systems that drive growth and protect their competitive advantages.